Testing the Limits of AI Safety
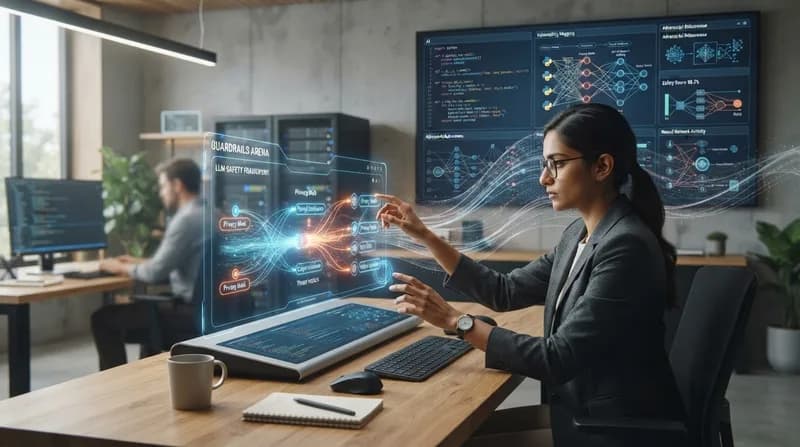
As large language models become increasingly integrated into enterprise workflows, the necessity for robust security has never been more critical. Hugging Face has officially launched the Guardrails Arena, a specialized platform designed to evaluate and challenge the efficacy of safety filters and privacy guardrails implemented in modern AI architectures. This initiative seeks to standardize how developers measure the resilience of their systems against sophisticated jailbreak attempts and unauthorized data extraction.
How the Arena Functions
The Guardrails Arena operates as a competitive space where researchers and developers can pit their security implementations against adversarial prompts. By crowdsourcing the challenge of 'jailbreaking' models, the platform generates a transparent leaderboard that tracks which safety frameworks successfully mitigate risk and which remain vulnerable to prompt injection or PII leakage. This transparency is intended to push the industry toward more rigorous, battle-tested security protocols.
Why It Matters
- Standardization: It provides a common benchmark for measuring AI safety, moving away from anecdotal security claims.
- Adversarial Learning: By exposing models to real-world attack vectors, developers can patch vulnerabilities before deployment.
- Privacy Focus: The arena specifically highlights the ability of guardrails to prevent models from leaking sensitive user information.
The launch represents a significant shift toward prioritizing security in the AI lifecycle. By focusing on the intersection of user privacy and system integrity, the Guardrails Arena serves as a critical infrastructure piece for those building production-grade AI agents. It forces the developer community to consider not just how well an LLM performs on reasoning tasks, but how effectively it adheres to strict safety boundaries under pressure. As these models move into higher-stakes environments, the insights gleaned from this arena will likely become the gold standard for enterprise-grade AI security compliance and risk management.