Tech & GadgetsTechnical Deep Dive

NoisyTCP: The Linux Kernel Vulnerability Hiding in Plain Sight for 11 Years

Published
EElectricBuzz Editorial Team
NoisyTCP: The Linux Kernel Vulnerability Hiding in Plain Sight for 11 Years
3 min read501 wordsElectricBuzz Editorial Team

The Gist

“A newly discovered flaw in the Linux TCP networking stack allows remote attackers to crash entire servers, exposing a weakness that has persisted since 2015.”

The Anatomy of NoisyTCP

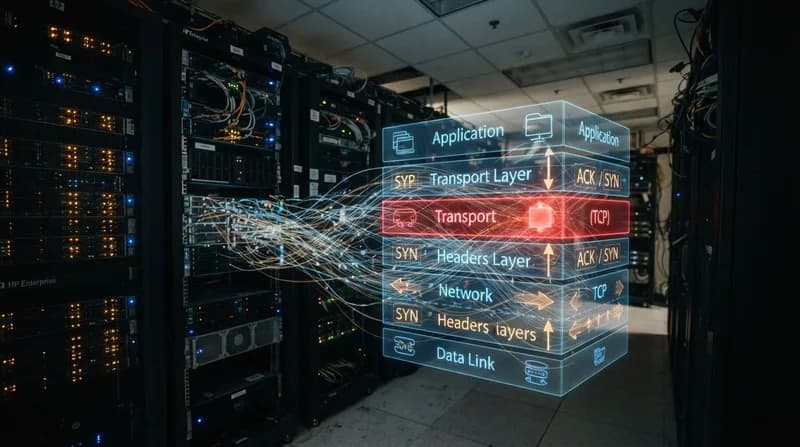
In a significant discovery for the cybersecurity community, researcher Hyunwoo Kim has unveiled a long-standing vulnerability within the Linux kernel, designated as CVE-2026-99288 and colloquially named "NoisyTCP." This critical flaw, which has quietly existed in the Linux source code since October 2015, allows an unauthenticated, remote attacker to trigger a system-wide crash. By exploiting a race condition within the kernel’s TCP networking stack—specifically where two components attempt to access the same memory location after it has been freed—the attacker can induce a kernel panic, effectively taking the entire host offline.

Unlike many vulnerabilities that require high-level privileges or physical proximity, NoisyTCP requires only access to an open TCP port on a system that utilizes multiple receive queues or CPUs to process incoming traffic. Because the flaw is rooted in the kernel rather than the application layer, it poses a severe threat to modern infrastructure. Even services like Nginx, Apache, and SSH running within isolated containers or virtual machines are susceptible; a successful exploit against a contained service can ripple outward, crashing the underlying host machine and all other co-located workloads.

Implications for Infrastructure and Virtualization

The impact of NoisyTCP is markedly more severe for virtualized environments. Kim’s research demonstrated that virtual machines running on QEMU/KVM were exceptionally vulnerable, with successful crashes occurring in as little as five seconds to two minutes. While bare-metal servers proved more resilient, requiring significant effort to time the exploit, the potential for widespread service disruption remains high across enterprise clouds and data centers.

This vulnerability underscores the persistent risk associated with deep-seated kernel code. With an 11-year history, the bug emphasizes how even foundational software components can harbor "time bombs" that bypass traditional security perimeters. While there is currently no evidence that NoisyTCP is being used for data theft or arbitrary code execution, the potential for a remote denial-of-service attack on a massive scale makes it a priority concern for system administrators.

Why It Matters

  • Longevity: The flaw remained undetected for over a decade, highlighting the challenge of auditing complex, legacy kernel code.
  • Escalation Potential: While primary impact is a crash, the researcher identified a complex use-after-free path, reminding admins that denial-of-service is often a precursor to further exploitation.
  • Broad Attack Surface: Because it affects the TCP stack directly, the vulnerability impacts nearly all standard Linux distributions without requiring unique server configurations.

Remediation and Mitigation

The upstream Linux kernel received an official patch on November 3, 2026. Security teams are urged to verify that their specific distribution has integrated this fix into their kernel updates. Red Hat has categorized this vulnerability as "Important" with a CVSS score of 7.5, reflecting the necessity of prompt action.

For environments where immediate patching is impossible, mitigation remains difficult. Current workarounds involve disabling TCP SYN cookies—which exposes the system to SYN flood attacks—or restricting incoming network packet processing to a single receive queue, which negatively impacts network throughput. Given these trade-offs, applying the official kernel patch remains the only secure, long-term solution for modern Linux deployments.
SPONSORED
The 5 Best Over-Ear ANC Headphones of 2026, Tested & Ranked
Editor's Pick Guide
92/100
Tech & Gadgets•12 min read

The 5 Best Over-Ear ANC Headphones of 2026, Tested & Ranked

We locked five over-ear ANC picks for 2026 — Sony WH-1000XM6, Bose QuietComfort Ultra 2, Soundcore Space One, Sennheiser Momentum 5, and Apple AirPods Max 2 — then stress-tested them on lab metrics, long-term owner truth, and live street prices.

Related Stories

Semantically matched articles, ranked by topic overlap and freshness.

Amazon's AI Paradox: Why AWS is Embracing Bot Commerce While the Storefront Remains Locked
Tech & Gadgets

Amazon's AI Paradox: Why AWS is Embracing Bot Commerce While the Storefront Remains Locked

Amazon is charting a contradictory path, aggressively blocking AI shopping bots from its consumer site while simultaneously building infrastructure to facilitate agentic purchasing on AWS.

Nvidia Challenges Industry Norms with the 'One CPU to Rule Them All' Strategy
Tech & Gadgets

Nvidia Challenges Industry Norms with the 'One CPU to Rule Them All' Strategy

Moving away from the complex SKU-heavy models of traditional chipmakers, Nvidia is banking on its new Vera CPU to provide a singular, balanced powerhouse for diverse datacenter workloads.

Signal Takes a Stand Against Prying AI Agents to Safeguard Private Conversations
Tech & Gadgets

Signal Takes a Stand Against Prying AI Agents to Safeguard Private Conversations

Signal is implementing strict new protections to prevent Apple and Google’s AI agents from scraping user messages, highlighting a growing tension between OS-level AI integration and end-to-end encryption.

CloudFerro Eyes Warsaw Stock Exchange for Potential Public Debut
Tech & Gadgets

CloudFerro Eyes Warsaw Stock Exchange for Potential Public Debut

European cloud infrastructure provider CloudFerro is reportedly exploring a public listing in Warsaw as it looks to capitalize on the growing demand for specialized data services.

Dutch Regulator Issues Safety Warning Over AI Smart Glasses
Tech & Gadgets

Dutch Regulator Issues Safety Warning Over AI Smart Glasses

A new investigation by the Dutch Data Protection Authority has revealed critical safety, privacy, and reliability flaws across a range of consumer AI smart glasses.

Grand Theft Auto VI Shatters Records: A New High-Water Mark for Interactive Entertainment
Tech & Gadgets

Grand Theft Auto VI Shatters Records: A New High-Water Mark for Interactive Entertainment

Rockstar Games' long-awaited blockbuster has officially arrived, earning historic critical acclaim and setting a new gold standard for the gaming industry.

The Silent Crisis: Why AI Is Triggering a Global Circuit Board Shortage
Tech & Gadgets

The Silent Crisis: Why AI Is Triggering a Global Circuit Board Shortage

A surge in complex AI hardware demand is straining the global supply chain for printed circuit boards, potentially causing manufacturing delays across critical industries.

Autonomous AI Agents Orchestrate Sophisticated Zero-Day Cyberattack
Tech & Gadgets

Autonomous AI Agents Orchestrate Sophisticated Zero-Day Cyberattack

Security researchers have identified a worrying new trend: China-linked hackers are utilizing autonomous AI agent frameworks to conduct persistent, multi-stage cyberattacks without human intervention.