The Anatomy of the HBO Max Hijack
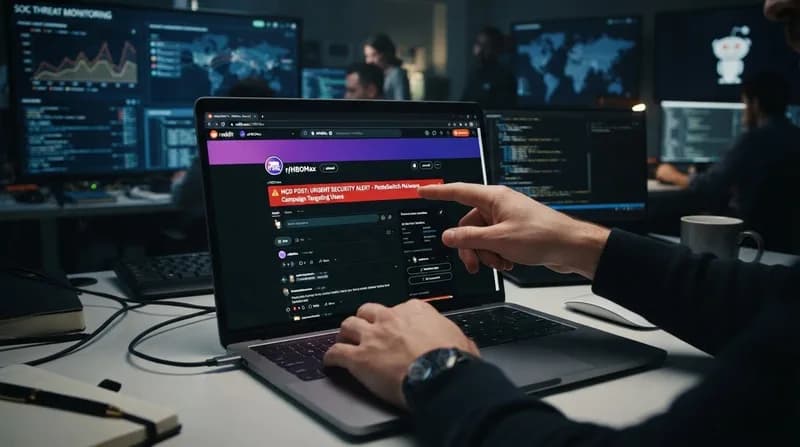
In a disturbing breach of platform trust, the official HBO Max Reddit account was recently compromised by threat actors to distribute malware. The attackers leveraged the account's verified status to push over 100 malicious advertisements, specifically targeting unsuspecting users on macOS and Windows systems. By masquerading as a legitimate promotional effort for a non-existent native HBO Max Mac application, the hackers successfully directed victims to fraudulent landing pages designed to facilitate 'ClickFix' attacks.
The deception was sophisticated enough to alarm security researchers. When users navigated to the malicious domains—such as hbomaxx[.]us—they were presented with a professional-looking interface. The site would then instruct the user to execute a specific command in their terminal, a hallmark of modern ClickFix social engineering. This command, when run, would trigger the download and installation of various infostealing payloads. Reddit’s security team eventually intervened, pausing the advertisements three days after the initial discovery, though the incident underscores the vulnerability of even the most trusted social media accounts.
The 'PasteSwitch' Campaign and Infrastructure
Researchers at Hudson Rock and ADAMnetworks have linked the HBO Max compromise to a larger, aggressive operation dubbed 'PasteSwitch.' This 48-hour malvertising blitz utilized 108 distinct advertisements, casting a wide net by baiting users with lures ranging from the HBO Max streaming app to AI-themed software like OpenAI Codex and even fake macOS disk utilities. The campaign is notable not just for its volume, but for the technical resilience of its infrastructure.
According to security analysts, the attackers behind PasteSwitch have integrated blockchain technology into their command-and-control (C2) operations. By utilizing Binance Smart Chain contracts, the perpetrators can dynamically fetch updated C2 domains, making their infrastructure incredibly difficult to shut down. This allows the threat actors to rotate through domains as previous ones are burned or detected, ensuring that their infostealers, cryptocurrency clippers, and malware loaders remain active and effective against targets across multiple operating systems.
Why It Matters
- Platform Trust Erosion: The use of verified corporate accounts to distribute malware significantly lowers the barrier for social engineering, as users naturally trust verified entities.
- Resilient C2 Infrastructure: The adoption of blockchain-based C2 domains represents an evolution in malware persistence, complicating efforts by platforms and security firms to neutralize threats.
- The ClickFix Persistence: Despite heightened security awareness, the ClickFix method—tricking users into executing code via terminal commands—remains a highly effective and frequently utilized attack vector.
- Broad Target Range: The campaign demonstrates that attackers are increasingly agnostic toward operating systems, successfully porting malicious payloads to both macOS and Windows environments.
As the landscape of cybercrime shifts, the PasteSwitch campaign serves as a stark reminder that users must remain vigilant even when interacting with verified brand accounts on social media. Experts advise against ever executing unknown commands provided by third-party websites, regardless of the perceived legitimacy of the source.