The Evolution of ASCII Smuggling
Historically, ASCII smuggling has been categorized as a specialized security concern within the realm of artificial intelligence. By utilizing invisible or non-rendering Unicode tag characters, threat actors could embed hidden instructions into documents or websites. When processed by a Large Language Model (LLM), these hidden prompts would trigger indirect injections, potentially causing the model to leak sensitive data or perform unauthorized operations. However, a recent discovery by Microsoft’s security team proves that these high-tech techniques are no longer confined to the AI ecosystem.
In a significant shift, cybercriminals have successfully adapted these smuggling methods for traditional phishing campaigns. By injecting Unicode tag spaces directly into text, attackers are effectively breaking up malicious keywords that would otherwise be caught by standard security filters. This evolution highlights a growing trend where techniques born in AI research are rapidly crossing over into established, legacy attack vectors, necessitating a more comprehensive approach to cybersecurity.
The Anatomy of the Phishing Campaign
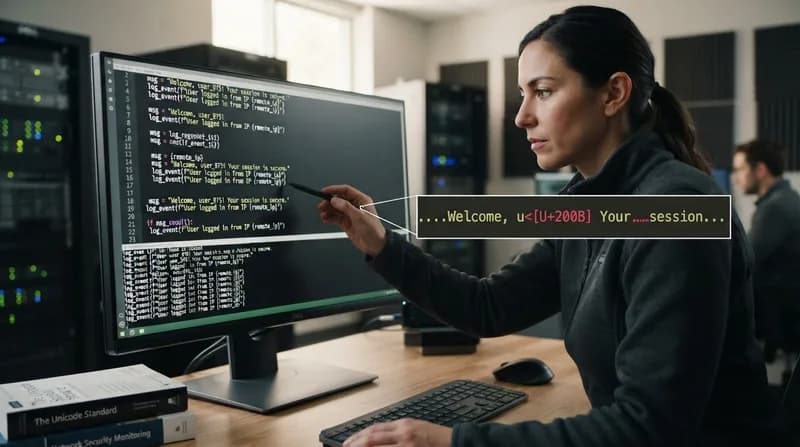
Microsoft’s investigation revealed a campaign of massive proportions, with peaks exceeding 2.37 million messages in a single day. The strategy was simple yet effective: attackers would insert Unicode tag spaces between the letters of common financial lures. For instance, the word "funding" would be obfuscated as "fun⟨U+E0020⟩ding." Because these tag characters are invisible to human users but processed as text by many systems, the split words pass through conventional keyword and regex-based filters that are not configured to look for non-rendering Unicode points.
The activity demonstrated a highly structured, almost corporate-like cadence. The campaign launched in early February, with volume surging from a few thousand to over 1.3 million messages in 24 hours. Researchers noted a distinct pattern: consistent, high-volume blasts during the work week followed by total silence on weekends. This "weekday-only" schedule persisted for three months before seeing a gradual decline by mid-June, suggesting an organized effort likely leveraging a network of roughly 150 disposable, finance-themed sender domains.
Why It Matters
This development serves as a wake-up call for security architects who have traditionally siloed AI security from standard email protection. The ability of threat actors to repurpose "AI-era" exploits to bypass legacy "pre-AI" filters underscores the fluidity of modern cyber warfare. Organizations that fail to account for how their ingestion pipelines process unconventional character sets are leaving themselves open to both direct phishing attacks and the next generation of AI-targeted exploits.
Defensive Implications and Mitigation
- Normalization Pipelines: IT departments must ensure that all email-processing systems perform rigorous normalization. This involves stripping or folding non-rendering Unicode code points before the content is evaluated by keyword or signature-based logic.
- Behavioral Analysis: As technical obfuscation becomes more sophisticated, reliance on signature detection alone is insufficient. Security teams should monitor for anomalous campaign behaviors, such as sudden spikes in volume from disposable domains or rigid, high-frequency patterns that mimic industrial work schedules.
- Cross-Domain Awareness: The blurring lines between AI prompt injection and traditional spam demonstrate that defenders must adopt a "cross-domain lens." Vulnerabilities in one platform are rarely isolated and often become the foundation for broader, multi-vector campaigns.