The Persistence of Mobile Tracking
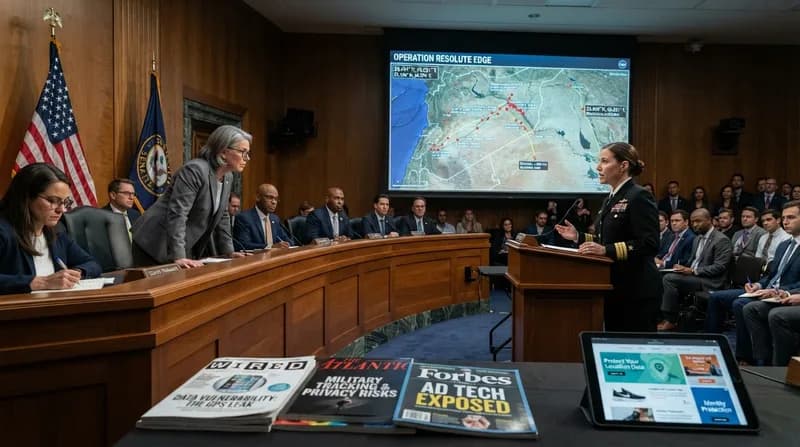
The United States Department of Defense (DoD) is facing renewed scrutiny as concerns mount over the ongoing availability of sensitive location data tied to military personnel. Despite concerted efforts to mitigate national security risks, lawmakers Senator Ron Wyden and Representative Pat Harrigan have formally requested an investigation by the DoD Inspector General. The inquiry seeks to determine why, despite the adoption of new security protocols, the movement of troops can still be tracked via commercially purchased data.
For years, the DoD has been aware that advertising software development kits (SDKs) and mobile applications act as conduits for data brokers, who aggregate location telemetry and sell it to the highest bidder. This marketplace creates a significant vulnerability, as adversaries could theoretically purchase this bulk data to pinpoint the locations of sensitive military installations or track the movements of personnel in active combat zones. While major military branches—including the Army, Air Force, Navy, Marine Corps, and Special Operations Command—have finally taken steps to disable mobile advertising identifiers (MAIDs) on government-issued hardware, the problem appears far from resolved.
Why it Matters: The Failure of Ad Identifiers
The core of this crisis lies in the mechanics of mobile advertising ecosystems. MAIDs were designed to provide advertisers with a persistent way to track user behavior across different apps and websites. However, security researchers have long highlighted that these identifiers act as "join keys," enabling data brokers to stitch together disparate datasets into a comprehensive profile of an individual's physical movements. Because these identifiers are broadcast across programmatic ad auctions, they are essentially visible to any participant in the ad tech market, including foreign entities that may be state-affiliated.
- Incomplete Implementation: Some DoD components only fully disabled these identifiers as recently as July, leaving a window of exposure for military movements.
- The "Personal Device" Loophole: Even if government-issued phones are secured, personnel and contractors often carry personal devices into secure facilities. These devices continue to leak location data through background app activity.
- Marketplace Proliferation: Ad-tech companies from nations with adversarial interests in the US may be harvesting this data through partnerships with common mobile applications, bypassing standard US regulatory oversight or data broker registries.
- Systemic Fragility: Security experts, such as Zach Edwards from Infoblox, have argued that simply disabling identifiers is a "defensive best practice" but may no longer be a sufficient safeguard against increasingly sophisticated tracking methods that do not rely solely on traditional MAIDs.
The Path Toward Accountability
The investigation requested by Congress serves as a critical stress test for the DoD’s cybersecurity policies. Lawmakers are now questioning whether the reliance on device-level settings is enough, or if a more radical shift in how personnel interact with mobile technology is required. The central fear remains that as long as the global advertising ecosystem continues to thrive on the commoditization of human movement, the most secure data will remain vulnerable to purchase by bad actors with the resources to aggregate it.
As the DoD Inspector General begins to untangle the flow of this data, the outcome may force a broader confrontation with the ad-tech industry itself. Without significant reform from major operating system providers like Apple and Google—who maintain these tracking ecosystems—the military may be forced to implement much stricter bans on personal mobile device usage in areas of strategic importance, fundamentally changing how service members stay connected in a digital age.