A New Era of Automated Vulnerability Discovery
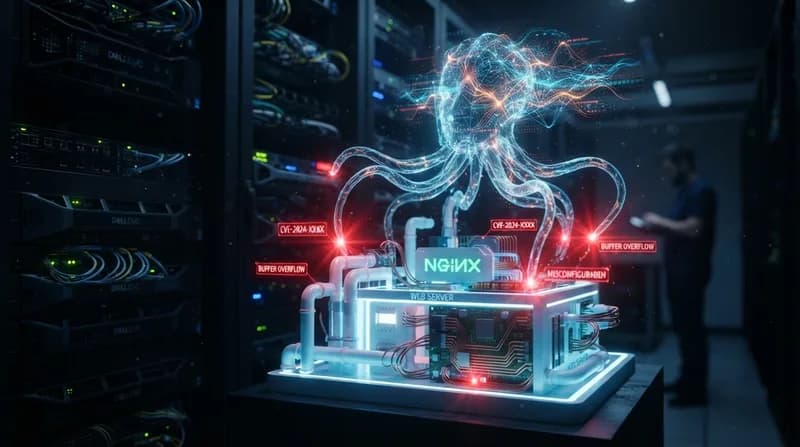
In a development that highlights both the promise and peril of modern cybersecurity, F5 has released emergency patches for ten distinct vulnerabilities discovered in the open-source NGINX web server. NGINX, which currently underpins approximately one-third of the world's websites—amounting to over 225 million instances—is a fundamental pillar of the internet’s traffic routing infrastructure. These flaws, several of which were identified using AI-driven research tools, include remote code execution (RCE) capabilities that could allow attackers to hijack servers, steal sensitive data, or paralyze services.
The discovery process underscores a broader trend in the security industry: AI is drastically accelerating the pace at which long-standing bugs are unearthed. One of the identified vulnerabilities, CVE-2026-123007, had reportedly been lurking in the codebase for over a decade, dating back to 2015. This revelation has prompted a massive, industry-wide scramble to update to version 1.31.9, the only release currently equipped with the necessary defensive mitigations.
The Critical Flaws: CVE-2026-123633 and CVE-2026-123007
Among the ten identified vulnerabilities, two stand out due to their high 9.2 CVSS severity rating. Both flaws are classified as critical and specifically target memory-safety mechanisms within the NGINX HTTP/2 implementation. According to researchers at Wiz, CVE-2026-123633 is a classic 'use-after-free' memory corruption issue, where the server attempts to access memory that has already been deallocated while a request is still active. This creates a window of opportunity for an attacker to manipulate the server's execution flow.
The second major concern, CVE-2026-123007, involves incorrect flow-control accounting which leads to invalid memory operations. Security researchers at Rapid7 have successfully demonstrated a proof-of-concept for this exploit, confirming that an unauthenticated remote attacker can achieve full remote code execution on vulnerable Linux-based NGINX deployments. Because these vulnerabilities require HTTP/2 to be active, they represent a significant risk to modern web infrastructure, which relies heavily on the efficiency of this specific protocol.
The "nginx2root" Threat and Future Implications
The security situation is further complicated by the discovery of an attack chain dubbed "nginx2root." Security firm Xint utilized AI-assisted scanning to uncover three additional NGINX flaws, which, when combined with a separate vulnerability in the underlying Linux kernel, allow an attacker to escalate privileges from a compromised NGINX process to full root access on the host server. This chain is effective across major cloud platforms including AWS, Azure, and Google Cloud, as well as on private bare-metal infrastructure.
Why it Matters
- Accelerated Discovery: AI tools are finding bugs in minutes that would have taken human researchers months to isolate, meaning the "patchapalooza" cycle is likely to continue.
- Foundational Risk: Because NGINX powers so much of the internet's traffic, even a small window of exposure can impact hundreds of millions of users simultaneously.
- System Hardening: While the current situation creates a logistical nightmare for sysadmins, proponents argue that this AI-driven pressure will eventually lead to more resilient, bug-free software as legacy codebases are aggressively audited and rewritten.
As the industry navigates this deluge of CVE disclosures, the consensus is clear: the speed of vulnerability discovery is now outpacing the industry's ability to deploy fixes. For now, system administrators are advised to prioritize upgrading to NGINX 1.31.9 or, at the very least, disabling HTTP/2 on public-facing servers until comprehensive security measures can be implemented.